Embedded Systems
When software meets hardware, assumptions become risk. Our elite adversarial operators tests embedded systems and IoT environments at the hardware, firmware, and protocol layers, exposing weaknesses attackers exploit in the physical and digital world. Our methodology helps manufacturers and operators build resilience into devices that cannot easily be patched or replaced.
Embedded Systems Overview
Ongoing testing of embedded and IoT devices, firmware, and communication interfaces to uncover firmware vulnerabilities, insecure protocols, hardware attacks, and supply-chain risks.

IoT Penetration Testing
Continuously test IoT devices and ecosystems to uncover exploitable weaknesses across firmware, networks, and APIs.
Methodology:
- Analyze device architecture, firmware, and embedded components
- Test device authentication, encryption, and update mechanisms
- Assess network communications, APIs, and cloud integrations
- Simulate real-world attacks against connected devices
- Deliver risk-ranked findings with actionable remediation guidance

Medical Device Security
Testing Assess medical device security to identify patient safety, data privacy, and regulatory compliance risks.
Methodology:
- Evaluate device firmware, hardware interfaces, and communications
- Test authentication, encryption, and access controls
- Assess interoperability with hospital networks and clinical systems
- Identify risks impacting patient safety and data integrity
- Deliver remediation aligned to FDA, HIPAA, and industry guidance
WHAT TO EXPECT?

Onboarding Platform
1

Align Objectives & Outcomes
2

Ongoing Testing / PIT Testing
3

Quarterly Service Review
4

Ongoing Testing Dashboard
5
Why Evolve Security?
01
CTEM Maturity Model
Evaluate CTEM maturity and strengthen resilience by assessing readiness against evolving adversary techniques and attack vectors.
02
CPT Market Leader
Offensive SOC and engineering experts drive measurable outcomes, guiding every phase from exposure discovery to remediation.
03
Award Winning Platform
Darwin Attack platform validates security controls and precisely pinpoints prioritized vulnerabilities across dynamic environments.
04
OffSec Operations Center (OSOC)
Agile bullpen of offensive testers rapidly adapts tactics, mirroring adversaries as threats and business priorities shift.
05
Trusted Methodologies
Industry-trusted methodologies including OWASP, OSSTMM, PTES, and NIST ensure disciplined, comprehensive penetration testing rigor.
06
Customized Simulations
Tailored simulations reflect an industry’s distinct threats, adversary behaviors, and mission-critical attack scenarios.
Game Changing Resources
Dive into our game changing resource library that delivers novel thought leadership and real-time perspectives that reimagine how organizations design, manage and elevate offensive security programs
The Signal, An Offensive Intelligence Digest (Volume 003)
The Signal Volume 003: Four of September's five most exploited flaws hit firewalls and VPN gateways. See the threat actors, CVEs, and fixes that mattered most in September 2026.
Evolve Security Joins Anthropic’s Cyber Verification Program
Evolve Security joins Anthropic's Cyber Verification Program, giving OSOC operators full, unthrottled Claude access for authorized red team and AI pen testing.
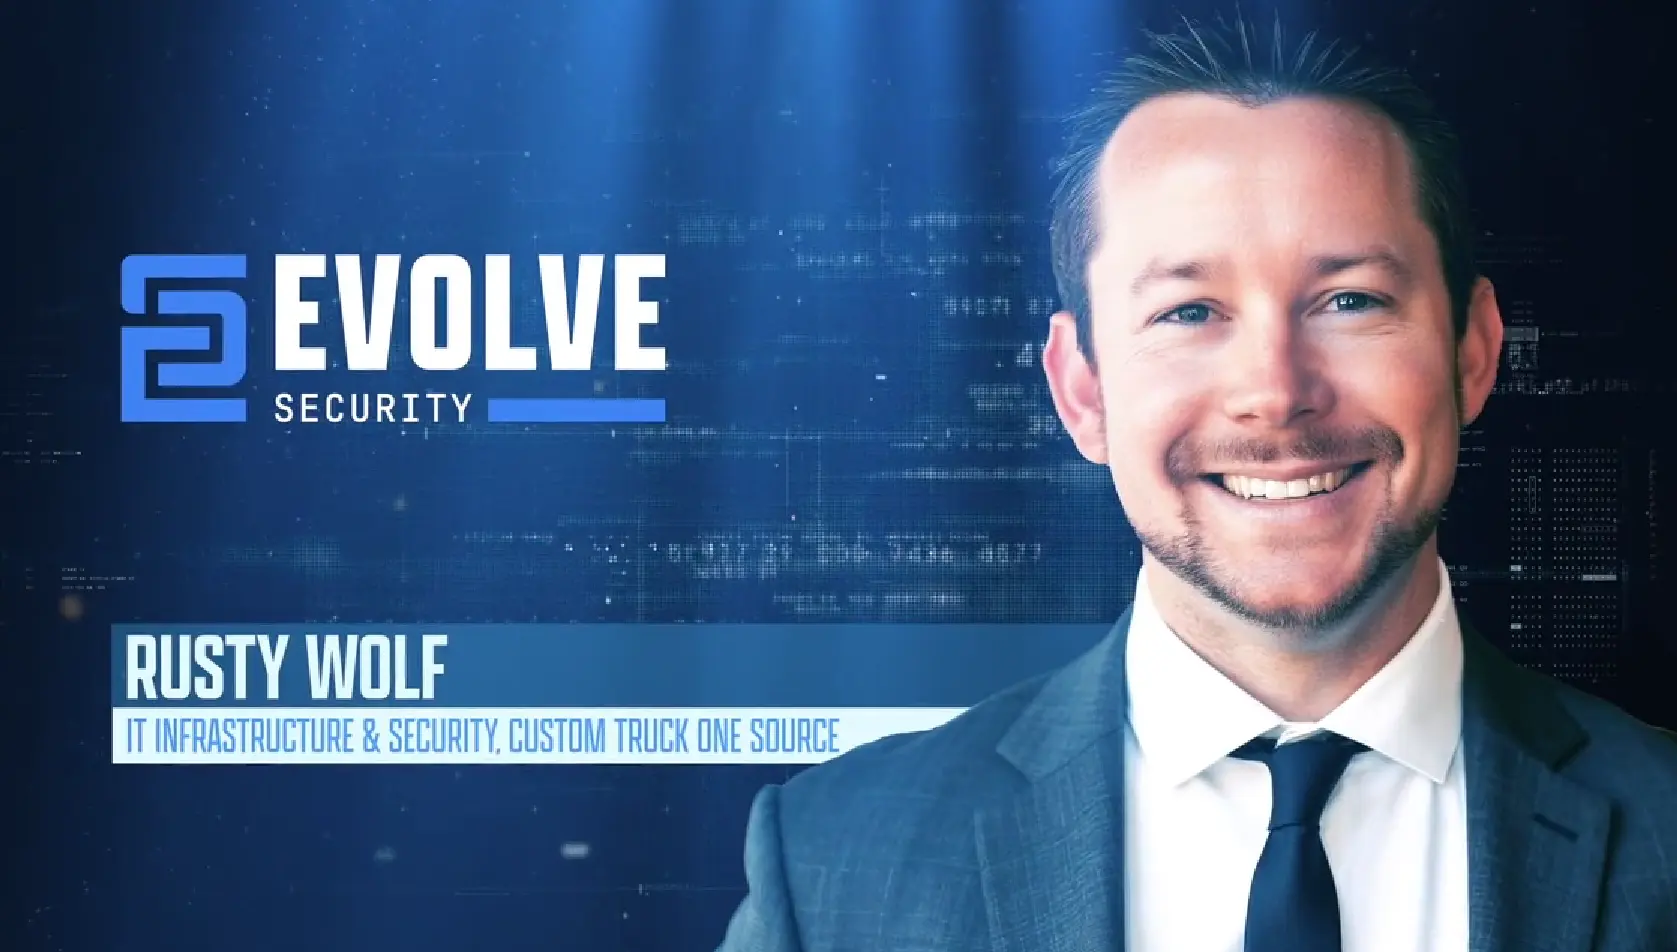
Rusty Wolf, Director of IT Infrastructure & Security, Custom Truck One Source
In this customer spotlight, Rusty Wolf, Director of IT Infrastructure & Security at Custom Truck One Source, sits down with Evolve Security to share what's kept the partnership strong, why continuous testing matters, and the value of human-in-the-loop validation.
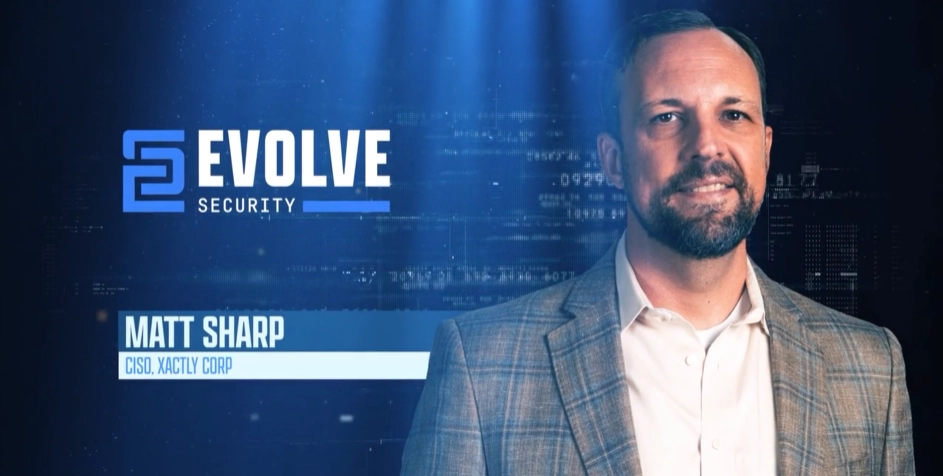
Matt Sharp, CISO, Xactly Corp
In this customer spotlight, Matt Sharp, CISO at Xactly, discusses how AI is reshaping the threat landscape, why Continuous Penetration Testing has become essential for modern security programs, the importance of human-in-the-loop validation, and how Evolve Security helps prioritize the exposures that matter most to reduce business risk.

Executive Dinner: Offensive Security in the Age of Frontier AI
Carnevor | Milwaukee’s Premier Steakhouse, Milwaukee, United States
Black Hat & Def Con 2026
Las Vegas
Is Anybody Safe? Adaptability in the Age of AI Disruption - with Mark Carney
Is any security company safe from AI disruption? Evolve Security CEO Mark Carney's answer: no and that's the wrong question anyway.
Pen Testing in the Age of AI: Man + Machine w/ Paul Petefish
AI is changing security fast. But is it replacing pentesters, or just giving them a powerful new co-pilot?