Superhuman. Offensive Security.

Building a resilient business begins by mimicking adversaries. Our continuous penetration testing solution, brought to life by Evo, provides the perfect blend of AI + Humans to emulate real-world scenarios, proactively finding and escalating risks with business context.

Continuous Threat Exposure Management

Three continuous disciplines, run from one Offensive Security Operations Center.
01

Attack Surface Management (ASM)

Continuous discovery of every internet-facing asset you own.
Evolve Security's attack surface management combines automated reconnaissance with expertvalidation. You get an accurate view of your external assets, exposures, and likely attack paths, so your team knows what an attacker can see.
02

Continuous Penetration Testing (CPT)

Ongoing penetration testing that keeps pace with your changing environment.
Evolve Security's continuous penetration testing pairs automated testing at scale with hands-on testing by offensive security experts. It finds vulnerabilities as your environment changes, shows how well your controls hold up, and gives you clear findings to act on.
03

Exposure Remediation (ER)

Turn findings into fixes.
Evolve Security's exposure remediation prioritizes and validates your security exposures. Using insights from continuous testing and monitoring, our experts help you fix critical weaknesses faster, before attackers can exploit them.

OFFENSIVE SECURITY SUITE

Identify exposures, validate vulnerabilities and assess your defenses with managed services, penetration testing services and advanced offensive security testing, all in one suite.

Managed Services

Ongoing visibility and expert guidance to help manage security risks.

Penetration Testing

Find exploitable weaknesses in your applications, cloud environments and networks.

Advanced Testing

Assess Al and embedded systems, and challenge your defenses with realistic adversary simulations.
Find the right approach for your organization.
Book a Demo
Compliance

Meet your compliance requirements. Then go further.

Continuous penetration testing and attack surface management that support the standards you answer to.

PCI DSS

Payment Card Industry Data Security Standard

SOC 2

System and Organization Controls

ISO 27001

Information security management

HIPAA

Health Insurance Portability and Accountability Act

HITRUST

Common Security Framework (CSF)

FedRAMP

Federal Risk and Authorization Management Program

Recognized as a
Leader and Outperformer
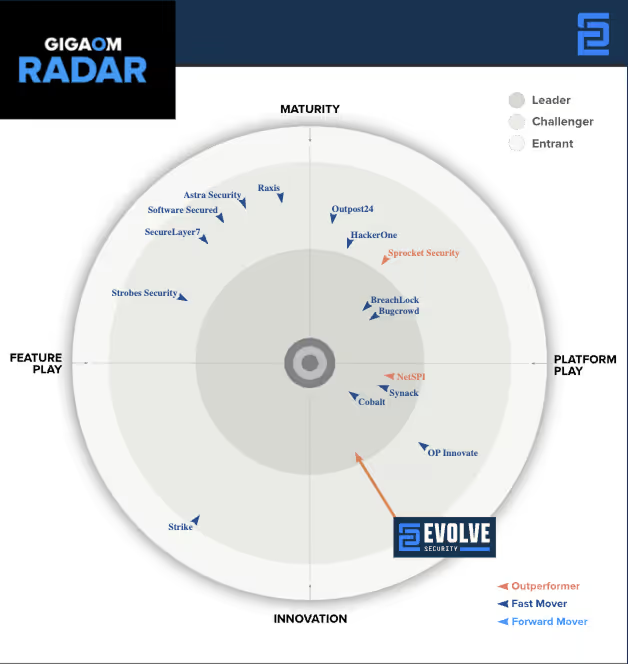
- GigaOm Radar for PTaaS

Recognized as 1 of 16 PTaaS leading vendors in the penetration testing market.
One of only two PTaaS vendors named both a Leader and Outperformer in the GigaOm Radar.
GigaOm Radar chart showing cybersecurity companies positioned by maturity and innovation with categories for Leader, Challenger, and Entrant, and annotations for Outperformer, Fast Mover, and Forward Mover.
OUR WINNING FORMULA

WHY TEAMS CHOOSE EVOLVE FOR PENETRATION TESTING

Evolve combines a testing platform with human ingenuity, depth, flexibility and dedicated service management. Here is what that means for your team.

CPT Platform

Our CPT platform facilitates advanced prioritization scoring of exposures based on the business function, criticality of an asset, attacker attractiveness, and threat intel.

Human Ingenuity

Dedicated Offensive SOC and engineering expertise driving outcomes and providing guidance from exposure identification through treatment.

Testing Depth

Utilizing offensive security experts as well as industry leading automation allows us to deliver both sophisticated testing and scale.

Custom +  Agile

Our engagement model allows us to quickly pivot activities based on business and threat landscape changes.

Service Management

Services team dedicated to achieving and maintaining alignment between business priorities and offensive security activities.
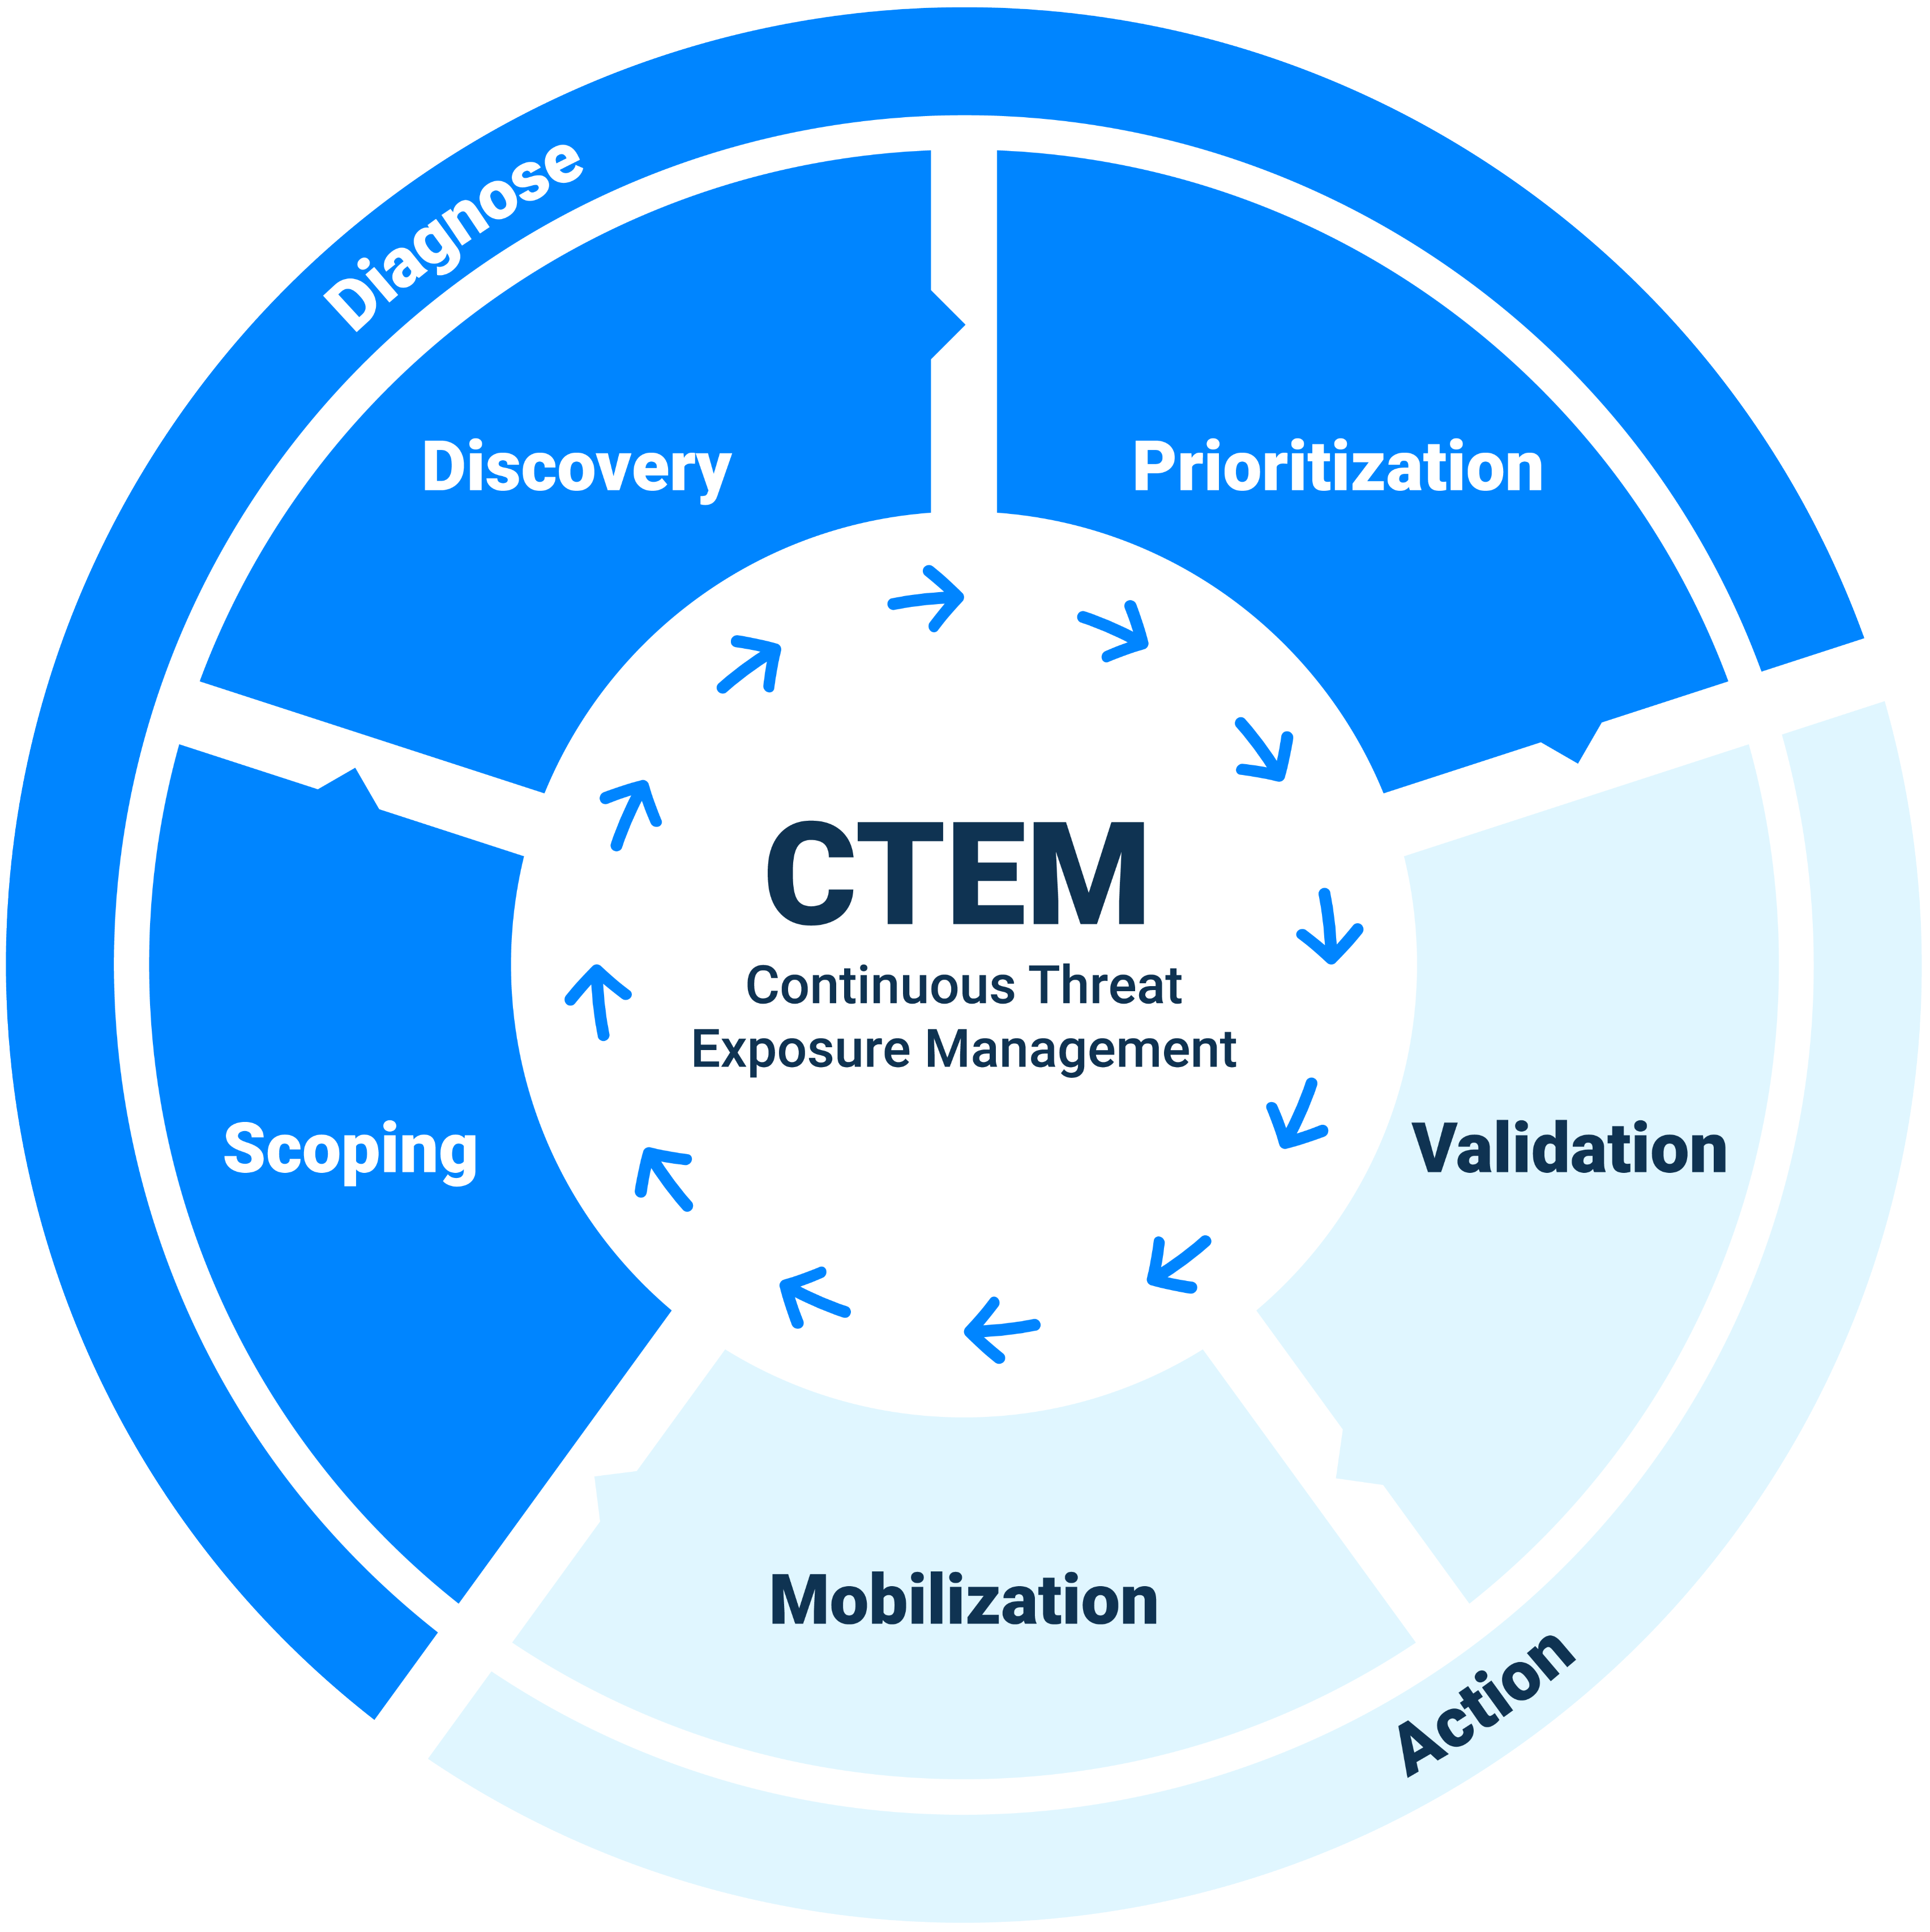
Circular diagram illustrating Continuous Threat Exposure Management (CTEM) with blue segments for Diagnose phase including Discovery, Prioritization, and Scoping, and light blue segments for Action phase including Validation and Mobilization.

CTEM isn’t just a buzzword

It's a programmatic solution built around 5 core steps. Evolve delivers it through continuous offensive security testing:

Scoping – Define what to test and protect

Discovery – Identify assets and exposures

Prioritization – Focus on what matters most

Validation – Simulate real-world threats

Mobilization – Drive remediation and action

Creating Raving Fans

At Evolve Security, our mission is to provide an unmatched customer experience from "the jump", our first interaction, and build a high-trust partnership with our customers along the journey
Xactly Corp
OPENLANE
Custom Truck
See More
OPENLANE, a leading digital marketplace for wholesale vehicles, partners with Evolve Security to manage its advanced offensive security program.
‍
In this customer spotlight, Rob, explains the importance of continuous penetration testing and how essential the human-in-the-loop element is to improve signal to noise ratio, identifying high-impact exposures and improving overall resilience.
Rob Tincher, Application Security Manager, OPENLANE

 Continuous Testing Resources

Dive into our game changing resource library that delivers novel thought leadership and real-time perspectives that reimagine how organizations design, manage and elevate offensive security programs

The Signal, An Offensive Intelligence Digest (Volume 004)

The Signal Volume 004: 5 CVEs exploited in the wild, 36 CISA KEV additions, and 3 threat actors, including two ransomware crews sharing one GlobalProtect flaw. Here’s what to patch first.

The Signal, An Offensive Intelligence Digest (Volume 003)

The Signal Volume 003: Four of September's five most exploited flaws hit firewalls and VPN gateways. See the threat actors, CVEs, and fixes that mattered most in September 2026.

Rusty Wolf, Director of IT Infrastructure & Security, Custom Truck One Source

In this customer spotlight, Rusty Wolf, Director of IT Infrastructure & Security at Custom Truck One Source, sits down with Evolve Security to share what's kept the partnership strong, why continuous testing matters, and the value of human-in-the-loop validation.

Matt Sharp, CISO, Xactly Corp

In this customer spotlight, Matt Sharp, CISO at Xactly, discusses how AI is reshaping the threat landscape, why Continuous Penetration Testing has become essential for modern security programs, the importance of human-in-the-loop validation, and how Evolve Security helps prioritize the exposures that matter most to reduce business risk.

Executive Dinner: Offensive Security in the Age of Frontier AI

Carnevor | Milwaukee’s Premier Steakhouse, Milwaukee, United States

Black Hat & Def Con 2026

Las Vegas

Is Anybody Safe? Adaptability in the Age of AI Disruption - with Mark Carney

Is any security company safe from AI disruption? Evolve Security CEO Mark Carney's answer: no and that's the wrong question anyway.

Pen Testing in the Age of AI: Man + Machine w/ Paul Petefish

AI is changing security fast. But is it replacing pentesters, or just giving them a powerful new co-pilot?