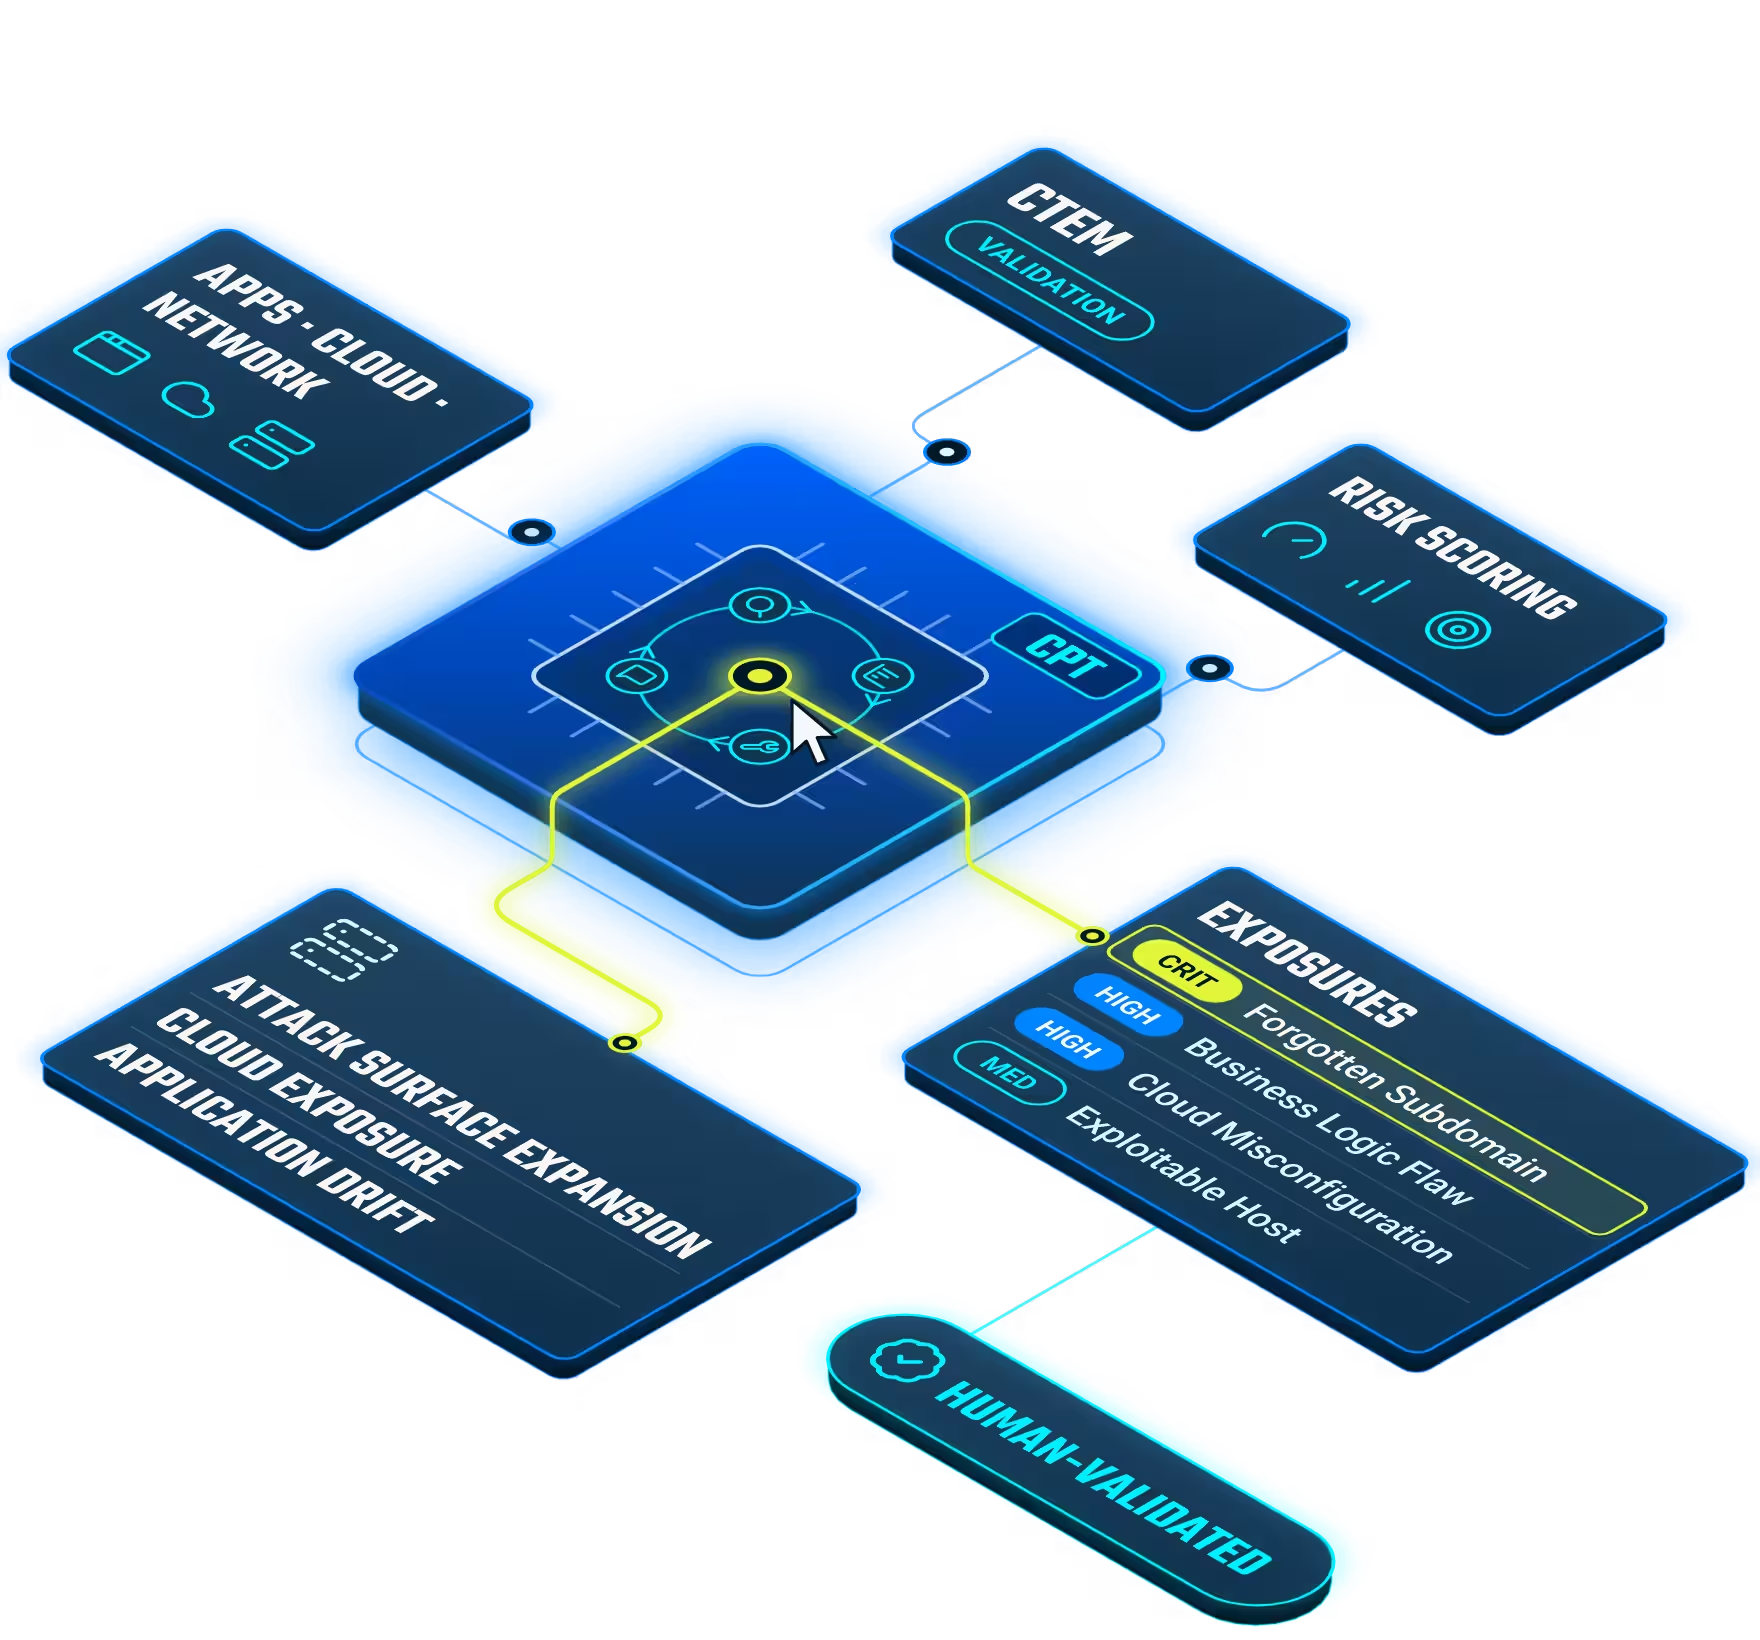
Continuously uncover and reduce digital attack exposure with proactive discovery, human-in-the-loop asset validation and actionable insights across all assets.
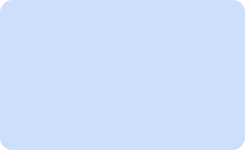
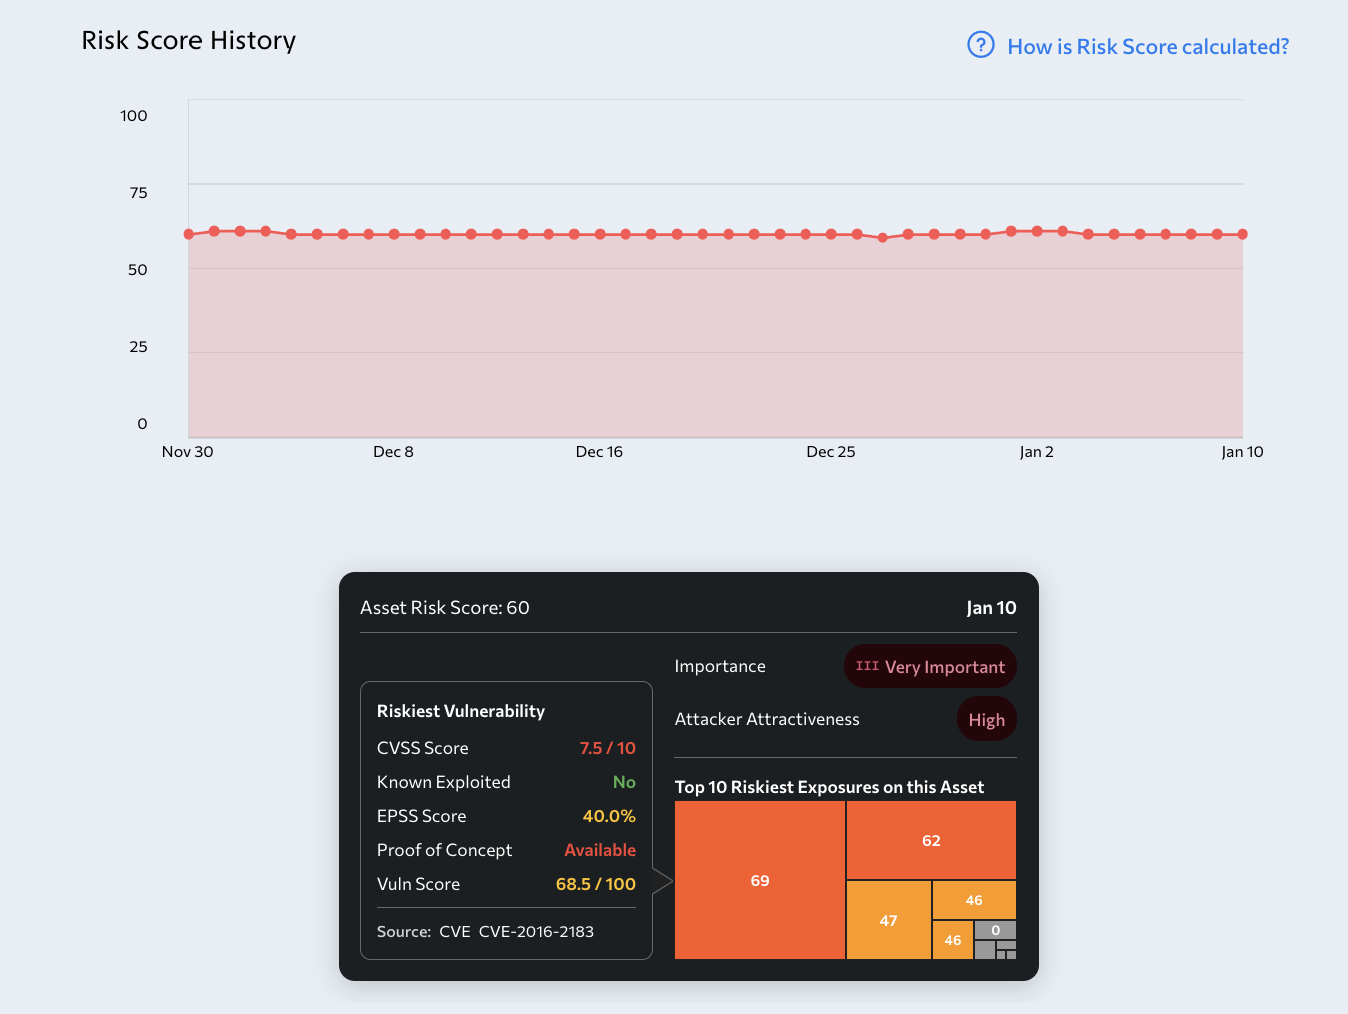
See how Risk Scoring turns raw exposure data into prioritized, business-relevant action, and why continuous penetration testing consistently outperforms the cost of a breach.
Our Managed Offensive Security Solution pairs human-in-the-loop expertise with AI to deliver ongoing penetration testing from our Offensive Security Operations Center (OSOC), validating exposures across your environment every day, not once a quarter.
1
Discover
Continuous attack surface discovery across all assets
2
Prioritize
Advanced risk-based prioritization of discovered exposures
3
Remediate
Pinpoint remediation actions across apps, cloud, and networks
4
Communicate
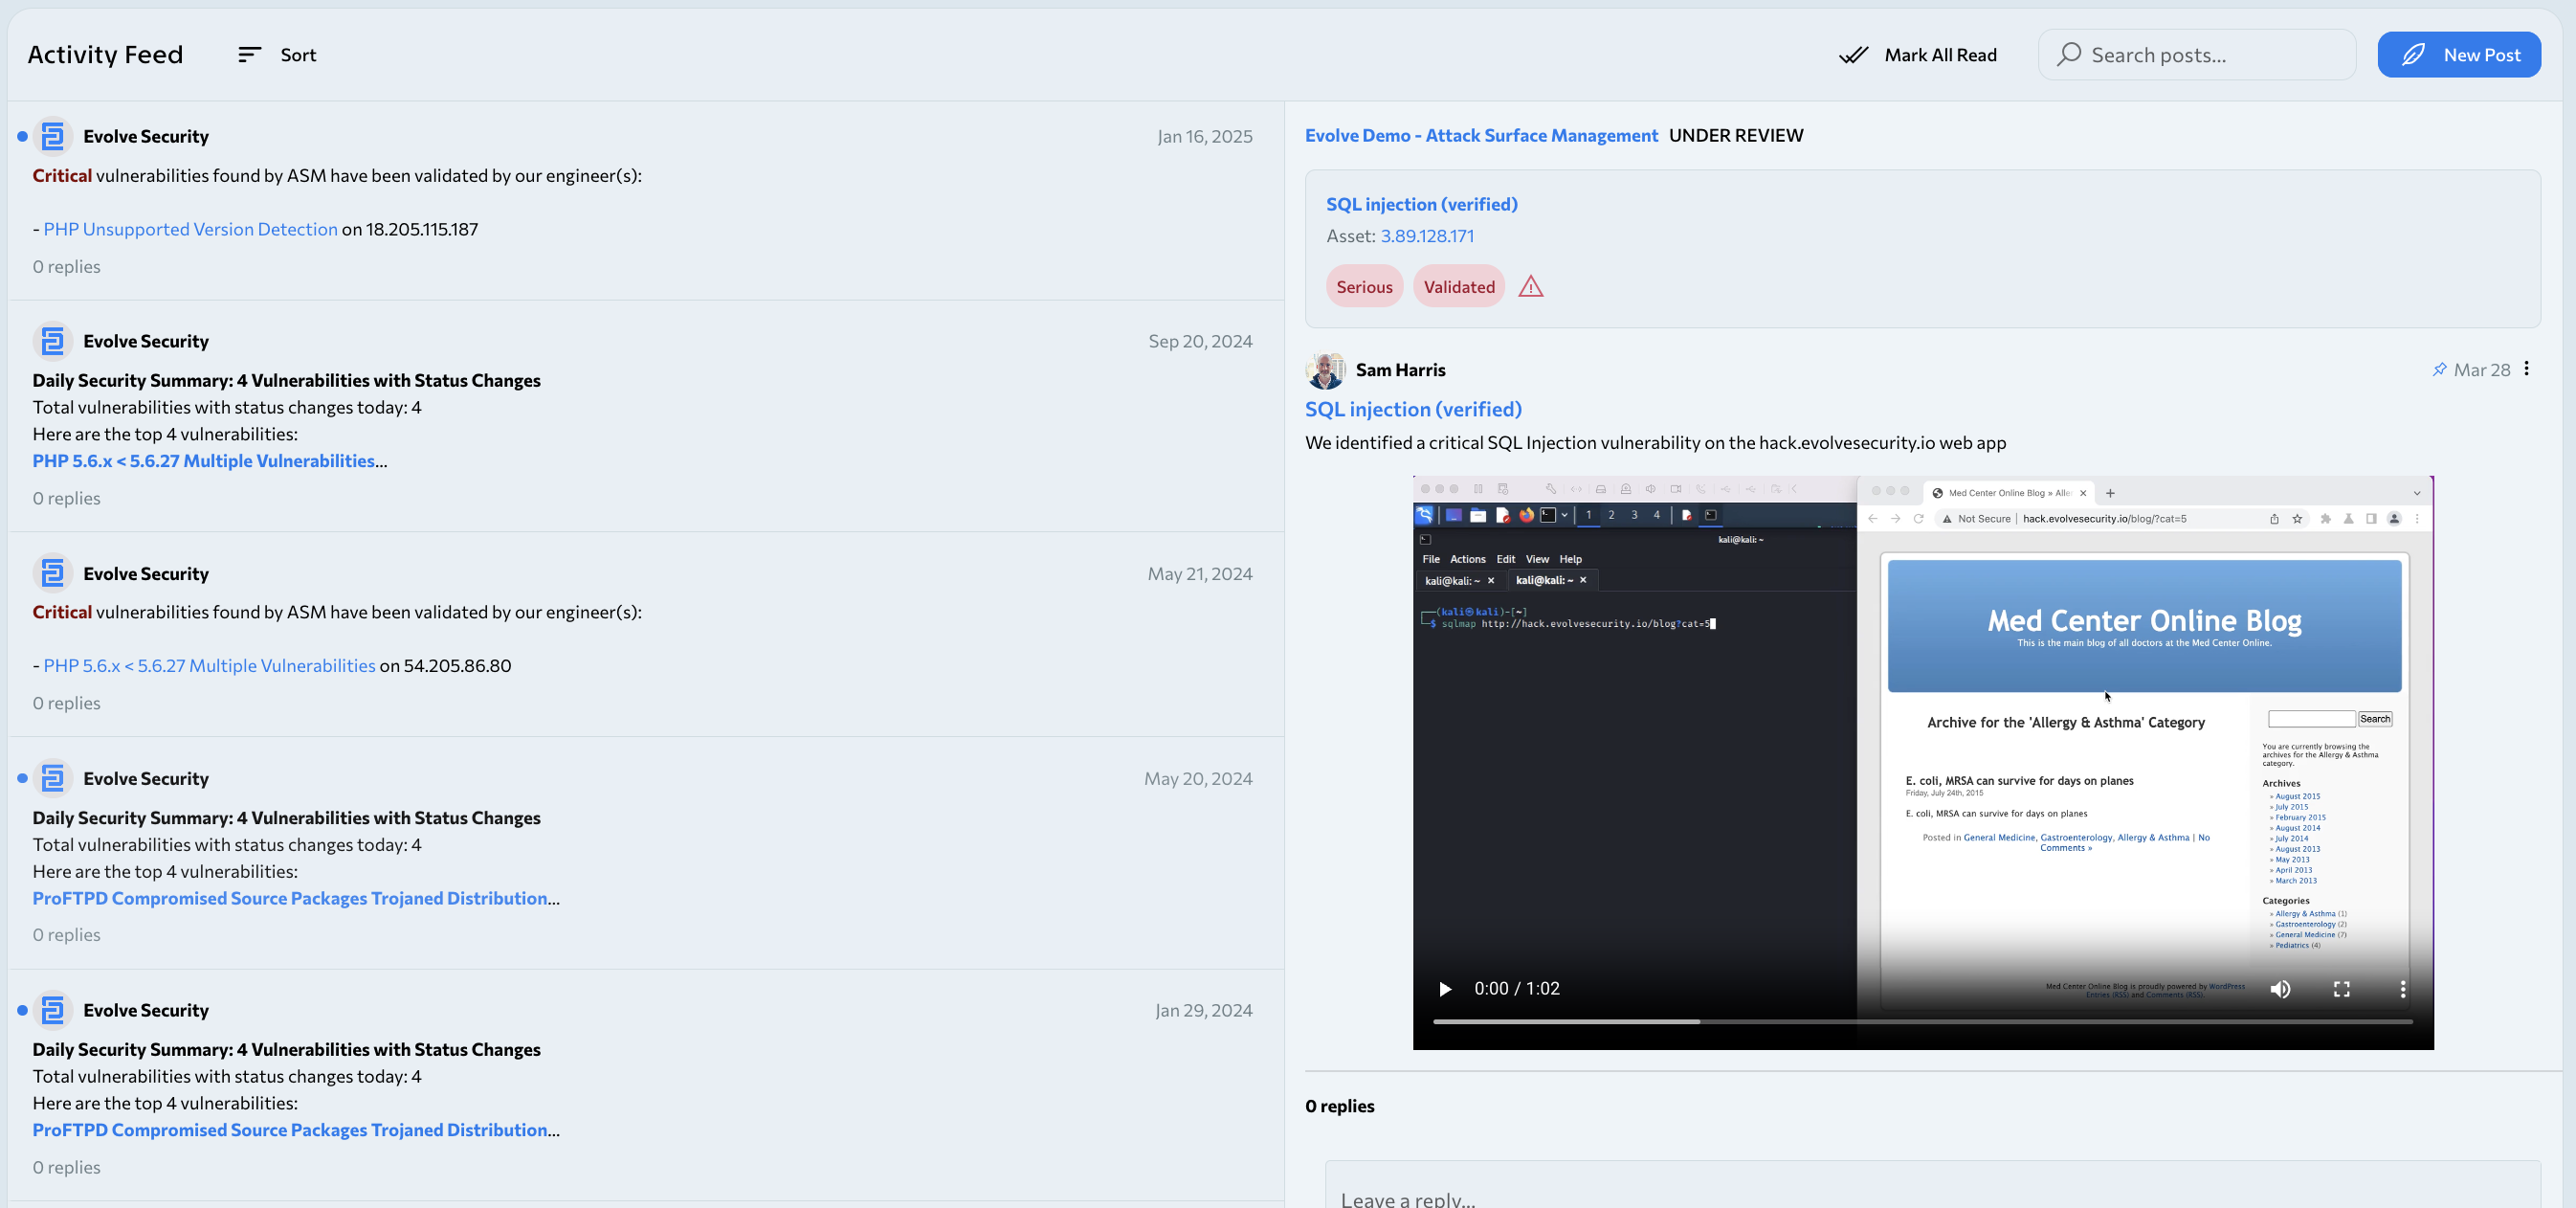
Real-time updates with client stakeholders throughout
The Continuous Advantage
Real-Time Discovery
Weaknesses surface the moment they emerge, not weeks later at your next scheduled assessment.
Shrinking Exposure Windows
Every day between a vulnerability's introduction and its fix is a day of risk. Continuous testing compresses that window from months to days.
A Proactive Security Posture
Shift from reactive, point-in-time audits to ongoing simulation of real adversary behavior so your defenses are tested the way they're actually attacked.
Built-In Compliance Readiness
Continuous validation means audit and regulatory evidence is always current, not scrambled together once a year.
Remediation That Actually Closes the Loop
Real-time reporting and retesting mean fixes get verified, not just filed, so "remediated" actually means remediated.
What Changes for Your Team
Less Noise, More Signal
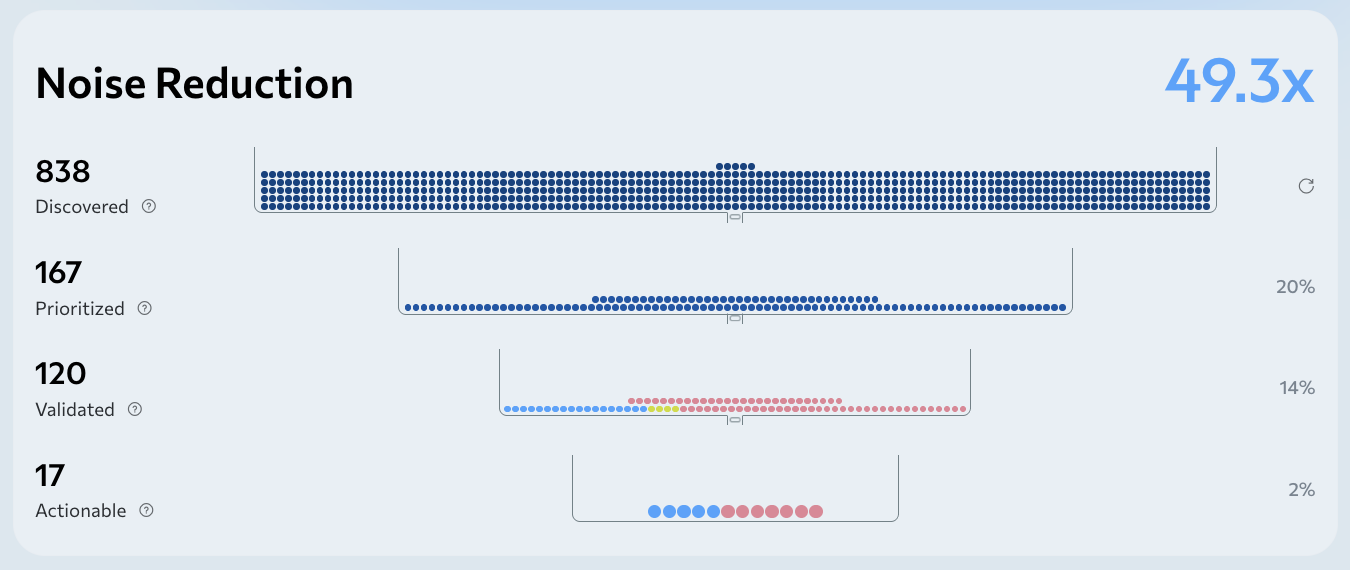
Actionable insights go up, irrelevant alerts go down, so your team spends time on real, high-impact threats instead of chasing false positives.
Defenses That Get Harder to Beat
By emulating real-world attacker tactics, techniques, and procedures, your security posture strengthens with every test cycle.
Proof of Progress, Not Just Promises
Repeatable evidence and clear metrics show measurable improvement against the risk indicators that matter to your board and auditors.
The Signal, An Offensive Intelligence Digest (Volume 003)
The Signal Volume 003: Four of September's five most exploited flaws hit firewalls and VPN gateways. See the threat actors, CVEs, and fixes that mattered most in September 2026.
The Signal, An Offensive Intelligence Digest (Volume 002)
The Signal Volume 002: 5 CVEs exploited in the wild, 29 CISA KEV additions, 4 active threat actors, including Lazarus Group and two ransomware operators. Here's what your team needs to patch first.
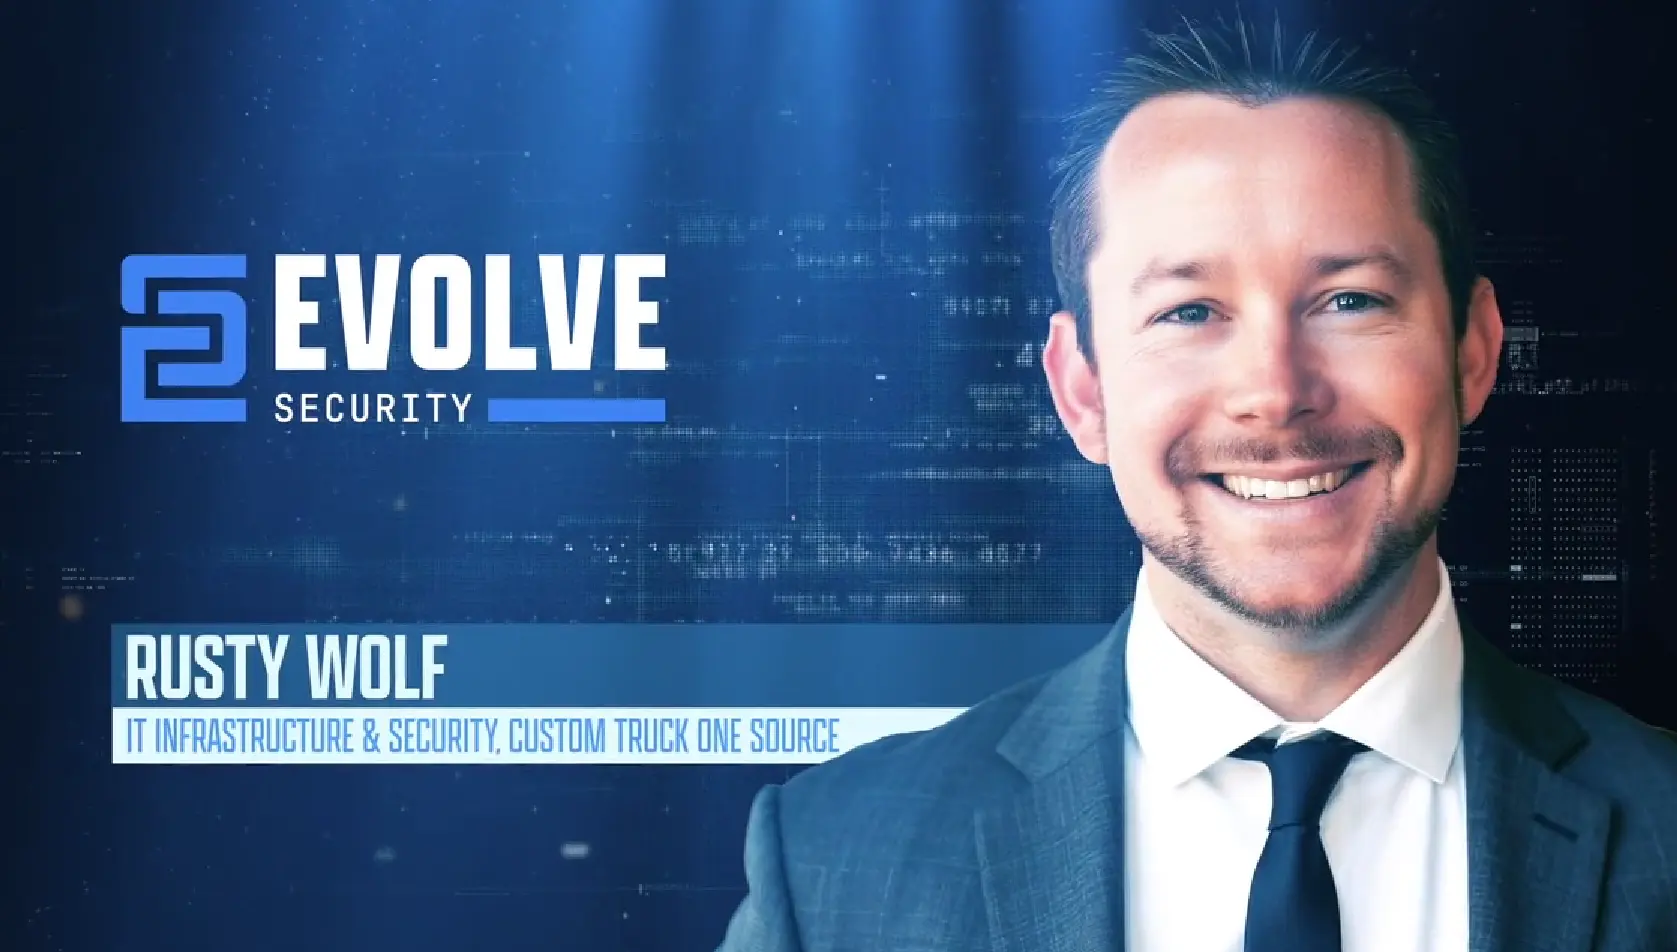
Rusty Wolf, Director of IT Infrastructure & Security, Custom Truck One Source
In this customer spotlight, Rusty Wolf, Director of IT Infrastructure & Security at Custom Truck One Source, sits down with Evolve Security to share what's kept the partnership strong, why continuous testing matters, and the value of human-in-the-loop validation.
SPOTLIGHT (E29) Continuous Motion; the Evolution of Offensive Security
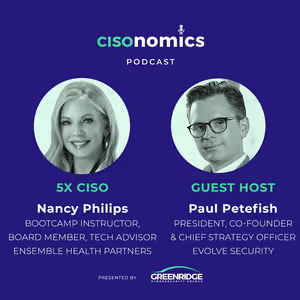
Joining from Black Hat to explore offensive security are 5X CISO Nancy Phillips of Ensemble Health Partners, and host Paul Petefish, President Co-Founder & Chief Strategy Officer of Evolve Security.
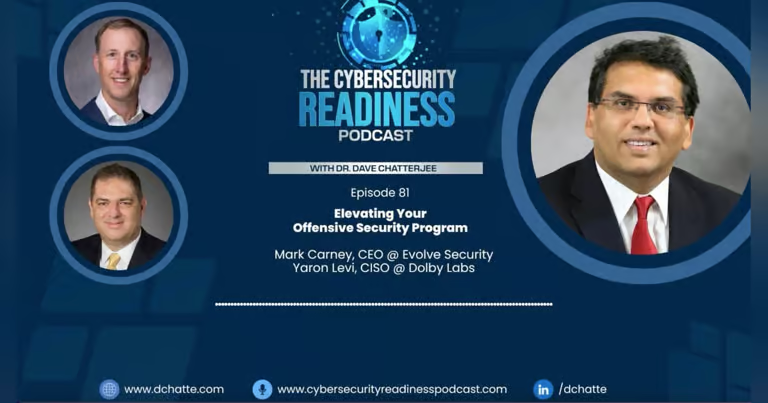
Dr. Dave Chatterjee hosts a discussion on elevating your offensive program with Mark Carney, CEO @ Evolve Security, and Yaron Levi, Chief Information Security Officer (CISO) at Dolby Labs.
We deploy code weekly, can annual pentesting even keep up?
No, and that's the exact gap continuous testing closes. Every release ships with unvalidated risk until your next scheduled test. Continuous testing validates changes as they go live, not months later.
We got breached through an asset we didn't know existed, how does this help?
Continuous testing pairs with ongoing discovery to catch shadow IT, forgotten subdomains, and orphaned assets before an attacker finds them first — not after a breach reveals the gap.
We just went through an acquisition and inherited infrastructure we don't fully understand, where do we start?
Continuous testing gives you immediate, ongoing visibility into inherited environments — surfacing exposures in newly acquired assets without waiting for a scheduled audit cycle.
Our last pentest report was outdated by the time we finished remediating it, how is this different?
Findings are reported and retested in real time as they're fixed, not batched into a single report that's stale on arrival. Remediation gets validated as it happens.
We're scaling fast and our security team can't keep pace — can this help without adding headcount?
Yes, continuous testing extends your team's coverage without new hires, handling ongoing validation so your internal team can focus on remediation instead of chasing test cycles.