Cloud Penetration Testing

How We Test Your Cloud Environment
Cloud Penetration Testing
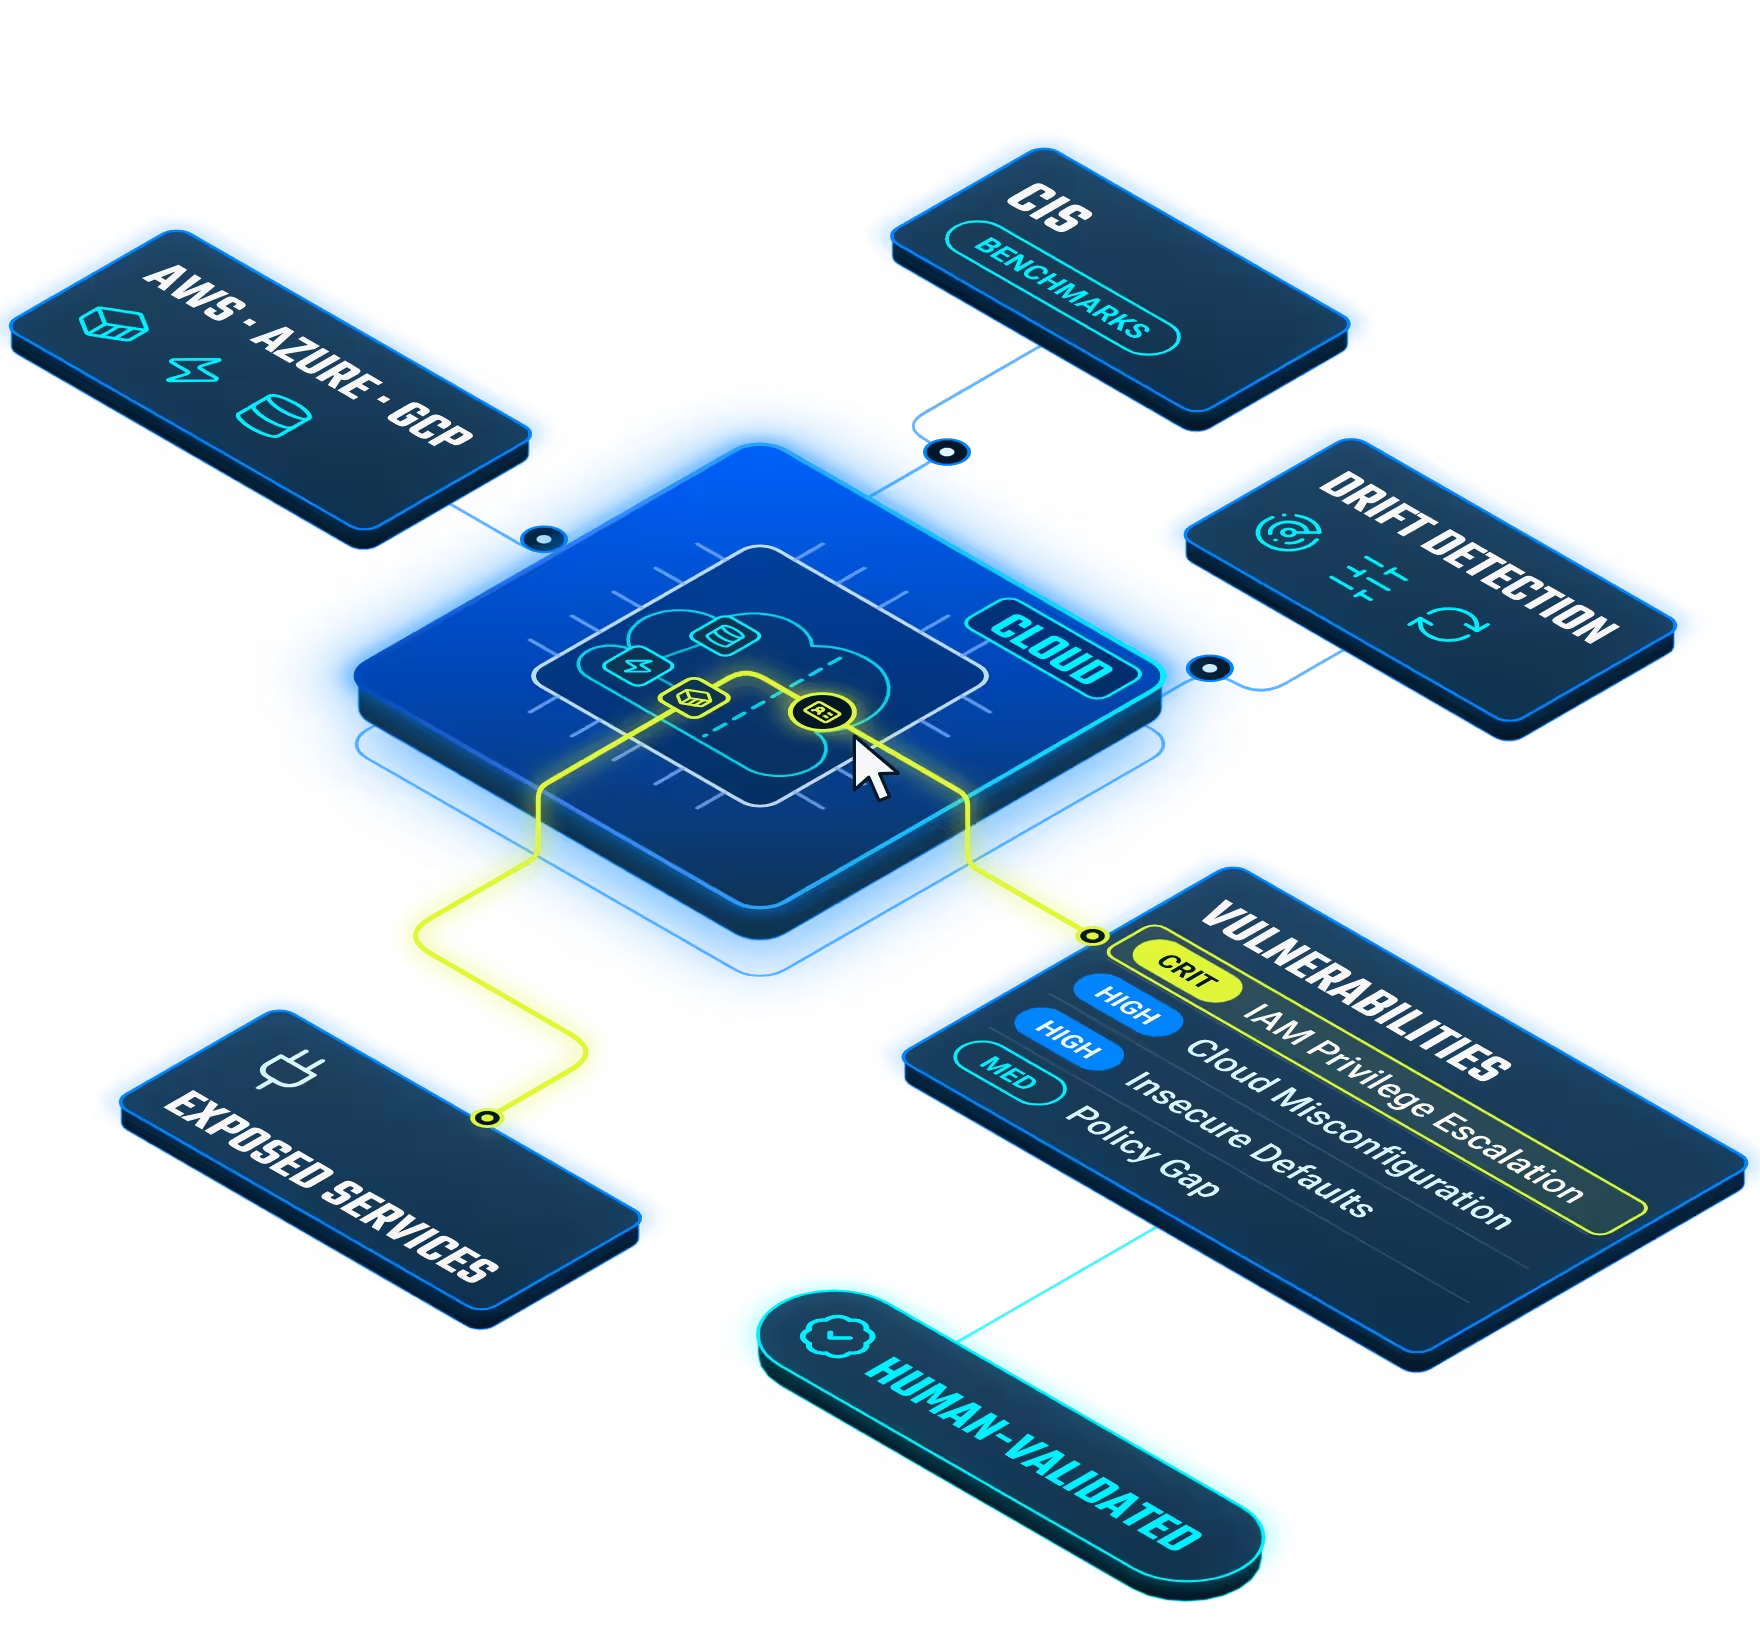
Test cloud environments - including AWS penetration testing, Azure penetration testing, and GCP penetration testing - to uncover exploitable weaknesses across infrastructure, identities, and workloads.
Methodology:
- Validate cloud IAM, identity trust paths, and privilege escalation risks
- Test exposed services, APIs, and network configurations
- Assess container, serverless, and workload security through cloud application security testing
- Simulate real-world attacker behavior across cloud attack paths
- Deliver prioritized remediation aligned to cloud provider best practices
Cloud Security Assessment
Assess cloud configurations and controls to reduce risk, misconfigurations, and compliance gaps.
Methodology:
- Review cloud architecture, configurations, and shared responsibility alignment
- Assess security posture against CIS, NIST, and cloud-native benchmarks
- Identify misconfigurations, insecure defaults, and policy gaps
- Evaluate logging, monitoring, and incident response readiness
- Provide risk-ranked findings with actionable remediation guidance
Our Cloud Testing Methodology
Scoping & Access
Configuration Review
Identity & Privilege Testing
Workload & Service Testing
Attack Path Validation
Reporting & Remediation Validation
Which Service Do You Need?
Cloud Penetration Testing
Attack Surface Management
Continuous Penetration Testing
Network Penetration Testing
Engagement Options
Continuous Cloud Penetration Testing
Point-in-time Cloud Penetration Testing
Testing Standards & Compliance
How we test
CIS Benchmarks
NIST SP 800-115
OWASP Cloud-Native Top 10
How Engagements Work
Every Cloud penetration testing engagement follows one connected process, from planning to retest.
Scope & Rules of Engagement
We agree on the accounts, subscriptions, and regions in scope, test windows, and what's off-limits before testing starts.
Test the Environment
Experts test identity, configuration, network, and workloads across AWS, Azure, and GCP, supported by the Darwin platform.
Validate Attack Paths
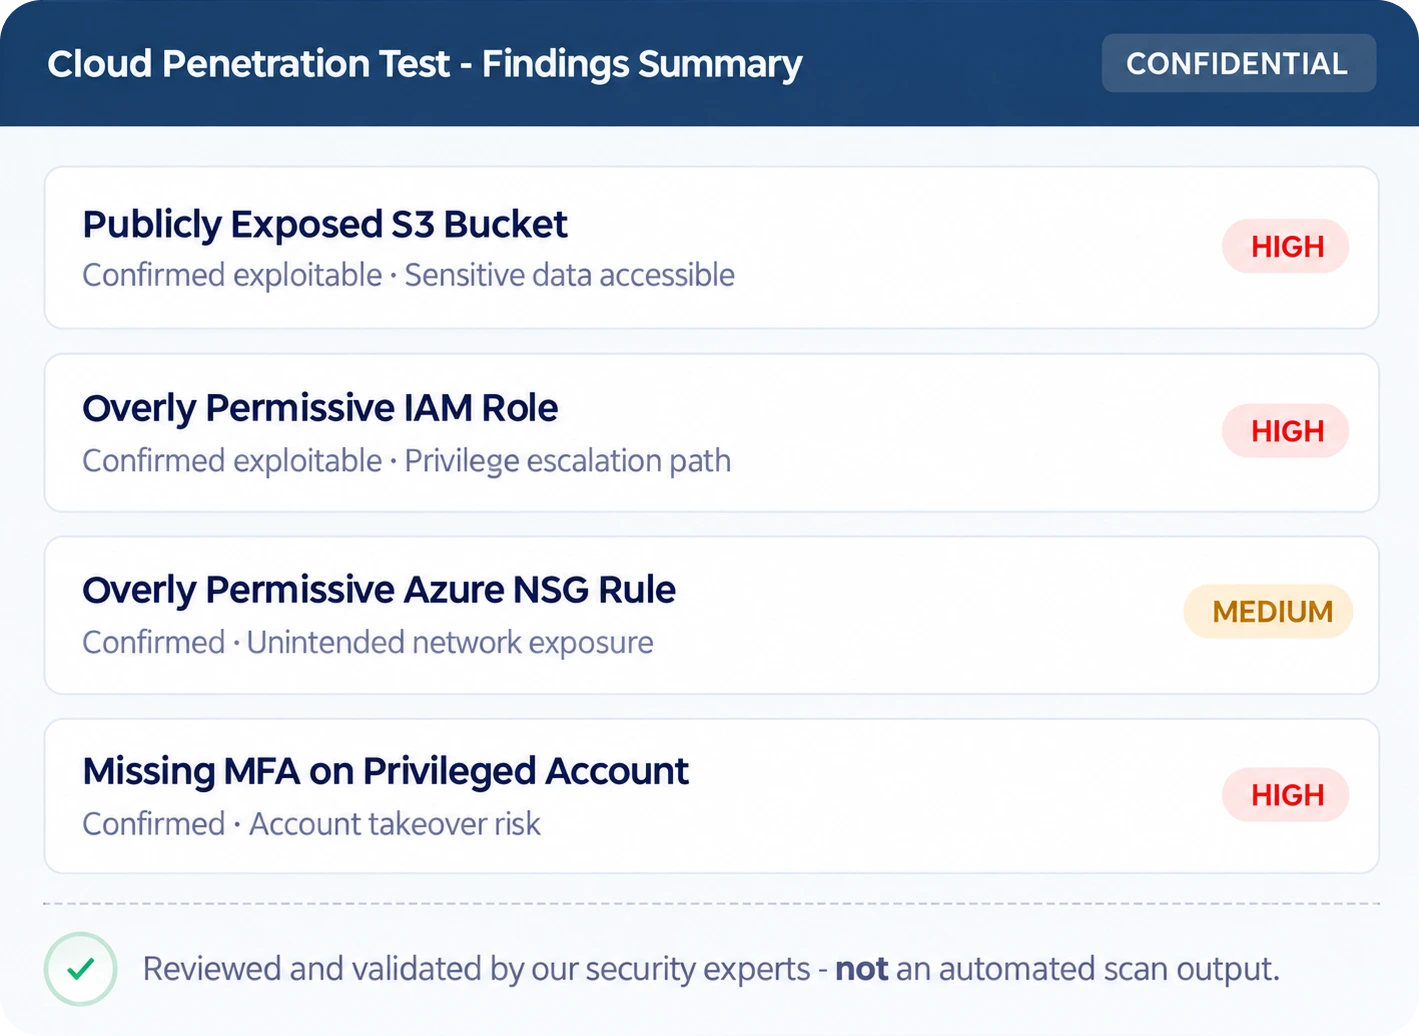
Every finding is confirmed as exploitable, showing how weaknesses chain from public exposure to sensitive data.
Report & Prioritize
A clear report with proof for each finding, ranked by real-world impact, with clear steps to fix.
Retest
After your team fixes an issue, we test again to confirm it's closed.
Results You Can Act On
Risk-ranked findings
Exploit evidence, not a CVE list
Prioritized remediation guidance
A retest to confirm the fix
Why Evolve Security?
01
CTEM Maturity Model
02
CPT Market Leader
03
Award Winning Platform
04
OffSec Operations Center (OSOC)
05
Trusted Methodologies
06
Customized Simulations
FAQ’s
Do you test across AWS, Azure, and GCP, or do we need separate engagements?
What's the difference between a cloud security assessment and cloud penetration testing?
Can you test our environment without disrupting production workloads?
What access do you need to our cloud accounts?
What do we receive when testing is complete, and is retesting included?
Can cloud and application testing be combined?
Do AWS, Azure, or GCP need to approve the test?
Continuous Testing Resources
Best Practices for Conducting AWS Penetration Tests
.avif)
Securing Azure Managed Identities: Understanding Risks and Implementing Mitigation Strategies

Rusty Wolf, Director of IT Infrastructure & Security, Custom Truck One Source
.webp)
Matt Sharp, CISO, Xactly Corp
Executive Dinner: Offensive Security in the Age of Frontier AI

Black Hat & Def Con 2026

Is Anybody Safe? Adaptability in the Age of AI Disruption - with Mark Carney