AI Penetration Testing

Trust AI systems that behave as intended, secure, resilient, and aligned. We test how AI actually fails - so your team knows before an attacker finds out.

How Does an Al Pentest Work?

See our step-by-step methodology for testing LLM apps, RAG pipelines, Al agents and the APIs and plugins around them.

HOW WE TEST AI AND LLM SYSTEMS

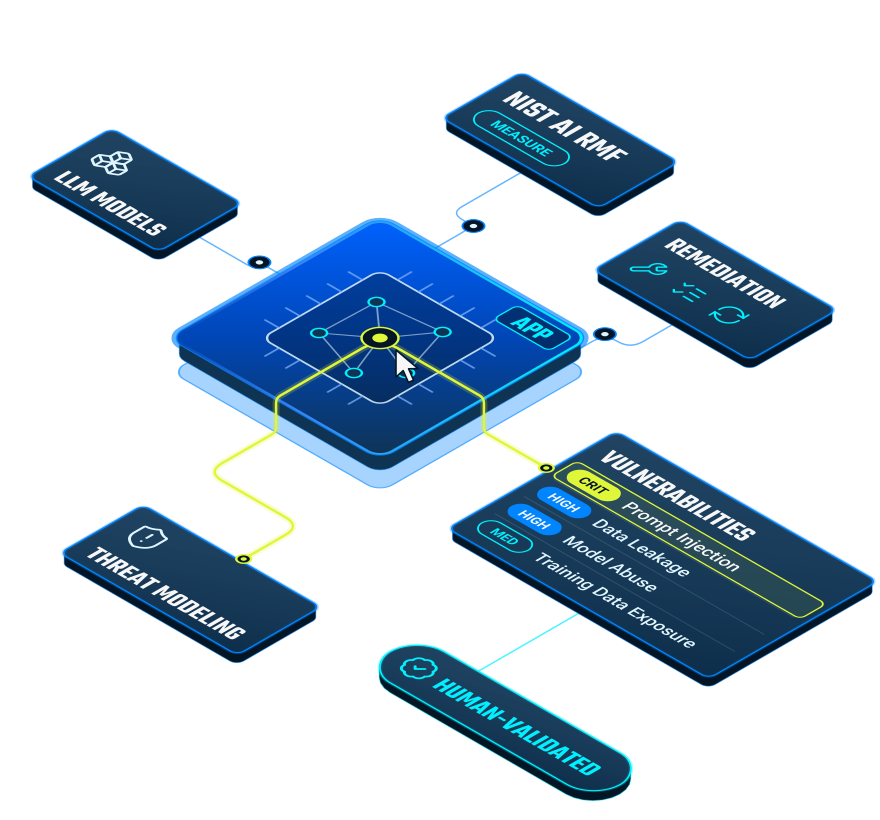
A hybrid approach blending AI governance, threat modeling and adversarial testing of models, including repeatable tests and remediation validation.
Blue circular icon with a white stylized robot face featuring two eyes and a mouth.

NIST AI RMF

Align AI systems to NIST AI RMF with structured risk identification, governance controls, and continuous validation.

Methodology:

  • Map AI use cases to NIST AI RMF core functions and risk categories
  • Assess governance, accountability, and model lifecycle controls
  • Evaluate data quality, bias, transparency, and explainability risks
  • Test model robustness, security, and operational resilience
  • Deliver prioritized remediation aligned to compliance and business impact
White microchip icon centered on a blue circular button with slight shadow.

Threat Modeling

Identify and prioritize AI-specific threats across models, data, infrastructure, and deployment environments, mapped to MITRE ATLAS.

Methodology:

  • Decompose AI architecture, data flows, and trust boundaries
  • Identify AI-specific threats (model abuse, poisoning, prompt injection)
  • Assess attacker impact, likelihood, and business risk
  • Map threats to controls and mitigation strategies
  • Validate findings through attack simulation and expert review

AI Penetration Testing

Simulate real-world attacker behavior, guided by the OWASP Top 10 for LLM Applications, to uncover exploitable weaknesses in AI models, APIs, and pipelines.

Methodology:

  • Test AI models, APIs, plugins, and orchestration layers
  • Execute prompt injection, data leakage, and model abuse scenarios
  • Assess authentication, authorization, and input validation controls
  • Evaluate training data exposure and inference risks
  • Deliver actionable findings with prioritized remediation guidance

Our AI Penetration Testing Methodology

From LLM penetration testing to AI security testing across your whole AI system, every engagement follows the same eight phases.
Step 01

Recon

01
How the LLM is used (RAG pipeline, etc.)
The user interface
The LLM provider
Step 02

Threat Modeling

02
STRIDE
OWASP Top 10 for LLMs
Step 03

Prompt Injection

03
Direct injection
Indirect / context injection
Multi-turn manipulation
Step 04

Input Validation & Context Filtering

04
Jailbreaking and filter bypass
Harmful or unsafe output
SQL / XSS injection in generated code
Step 01

Output Injection & Reflection

01
HTML / JS injection in the frontend
Command injection
Prompt leaks
Step 06

API & Plugin Security

06
Authorization
API key exposure
Command chaining or misuse
Step 07

Data Leakage & Privacy

07
User data
Internal documents
System prompts or embeddings
Step 08

Adversarial Input Testing

08
Unicode tricks and typosquatting
Multi-language manipulation
Poisoned docs in RAG systems

Powered By Our Darwin Attack Platform

Every finding from this engagement is tracked in Darwin, from discovery through retest, giving you a live view of your Al risk instead of a static report that goes stale the day it's delivered.

Which Service Do You Need?

AI testing overlaps with three other services. Here is how they differ, so you can choose the right one.

AI Red Teaming vs. Traditional Penetration Testing

Al systems still run on code, APIs, and infrastructure - traditional testing still matters. Al-specific testing adds coverage for attack surfaces conventional pentesting doesn't reach.

Al Red Teaming & Penetration Testing

Attack surface
Prompts, training data, model behavior, RAG pipelines, Al agents
Frameworks referenced
NIST AI RMF, OWASP Top 10 for LLM Applications, MITRE ATLAS
catches that the other misses
Model abuse, prompt injection, data leakage from training data or context
vs

Traditional Penetration Testing

Attack surface
Code, APIs, identity, infrastructure, access controls
Frameworks referenced
OWASP Top 10, PTES, OSSTMM
catches that the other misses
Traditional injection flaws, broken auth, access-control gaps
Choose your model

Engagement Options

Choose the AI penetration testing model that fits how often your AI changes.

Testing Standards & Compliance

Our model security testing follows proven AI frameworks, from the first test scenario to the final report.

How we test

The methodologies that shape every enagement

NIST AI RMF

U.S. standard framework for building and using AI that’s trustworthy, secure and accountable.

OWASP Top 10 for LLM Applications

The most common LLM risks, used to shape test scenarios.

MITRE ATLAS

Real-world AI attack techniques, used to map threats and findings.
The Process

How Engagements Work

Every AI penetration testing engagement follows one connected process, from planning to retest.

Scope & Rules of Engagement

We agree on the models, prompts, integrations and environments in scope, test windows, and what's off-limits before testing starts.

Test the Environment

Experts map your AI architecture and threats, then test models, prompts, RAG pipelines and agents by hand, supported by the Darwin platform.

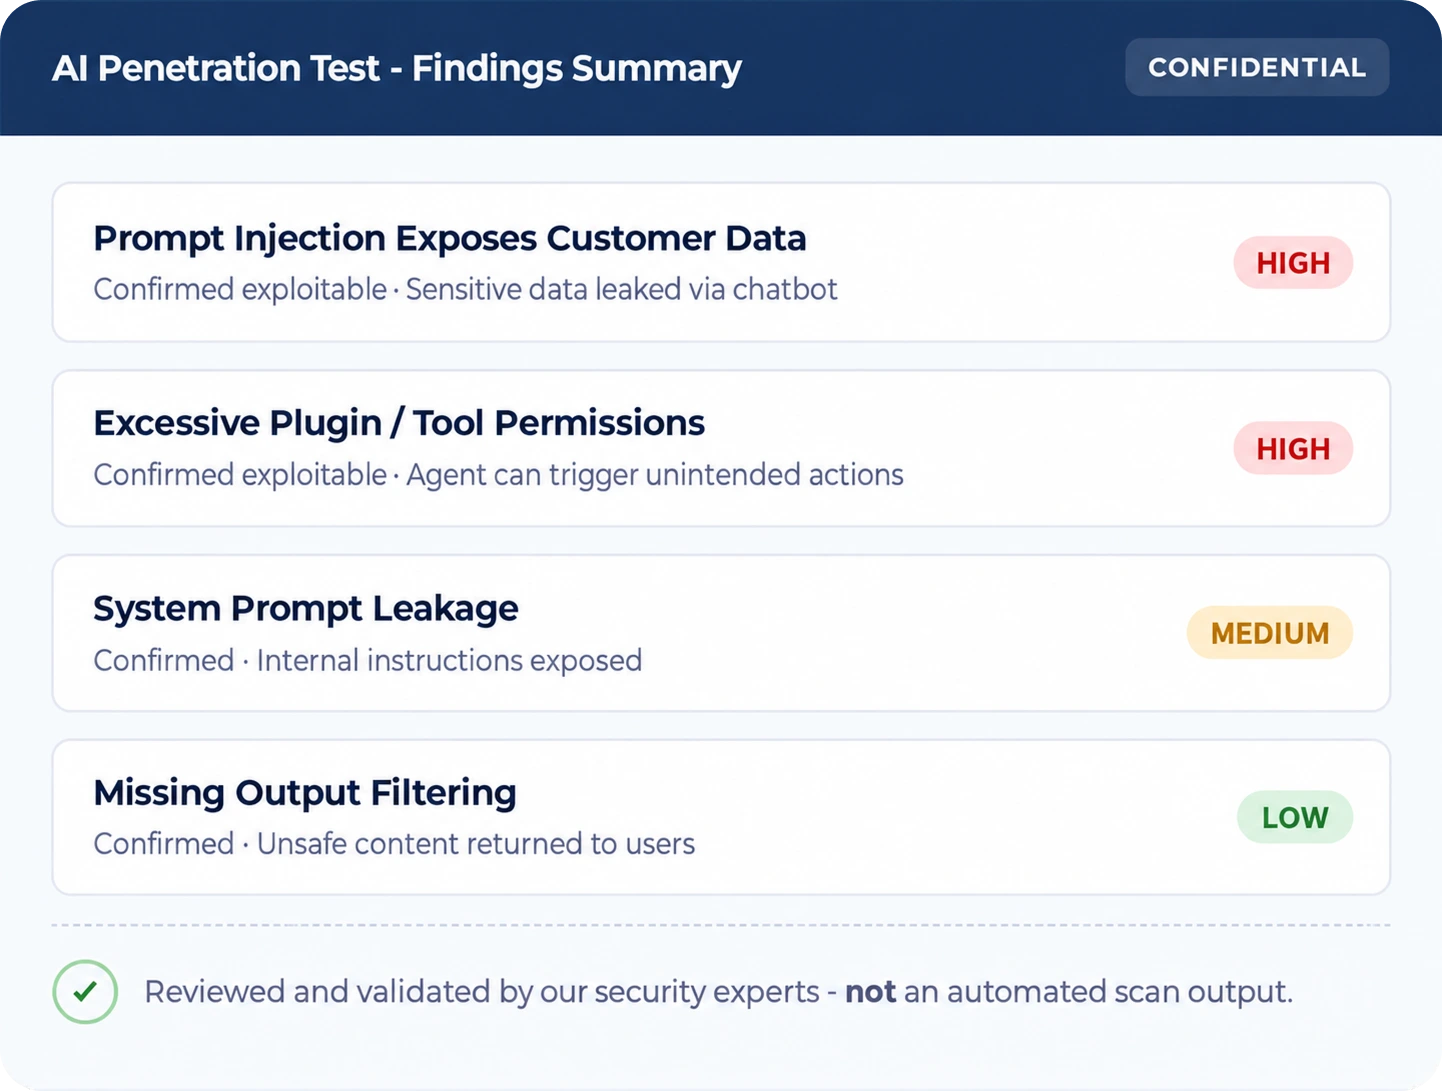
Validate Attack Paths

Every finding is confirmed as exploitable, showing how prompt injection or model abuse could lead to data exposure or unwanted actions.

Report & Prioritize

A clear report with proof for each finding, mapped to the OWASP LLM Top 10 and MITRE ATLAS, ranked by real-world impact.

Retest

After your team fixes an issue, we test again to confirm it's closed.

WHAT YOU GET

Results You Can Act On

Every engagement ends with more than a list of vulnerabilities. Here's exactly what lands in your hands when testing wraps.

Risk-ranked findings

Ordered by real-world exploitability and business impact, not just CVSS score

Exploit evidence, not a CVE list

Proof-of-concept steps showing how each finding was actually exploited

Prioritized remediation guidance

Clear next steps for your AI and engineering team, ordered by what to fix first

A retest to confirm the fix

We verify each issue is actually closed, not just marked resolved

Why Evolve Security?

01

CTEM Maturity Model

Evaluate CTEM maturity and strengthen resilience by assessing readiness against evolving adversary techniques and attack vectors.

02

CPT Market Leader

Offensive SOC and engineering experts drive measurable outcomes, guiding every phase from exposure discovery to remediation.

03

Award Winning Platform

Darwin Attack platform validates security controls and precisely pinpoints prioritized vulnerabilities across dynamic environments.

04

OffSec Operations Center (OSOC)

Agile bullpen of offensive testers rapidly adapts tactics, mirroring adversaries as threats and business priorities shift.

05

Trusted Methodologies

Industry-trusted methodologies including OWASP, OSSTMM, PTES, and NIST ensure disciplined, comprehensive penetration testing rigor.

06

Customized Simulations

Tailored simulations reflect an industry’s distinct threats, adversary behaviors, and mission-critical attack scenarios.

FAQ’s

We use OpenAI's or Anthropic's API, not our own model. Are we still at risk?

Yes. Most AI risk sits in how your product uses the model: prompts, plugins, RAG pipelines and APIs. Our LLM penetration testing covers prompt injection testing, data leakage and RAG misconfigurations at this integration layer, not just the model.

How is AI penetration testing different from a normal web app pentest?

A standard web application pentest doesn't cover prompt injection, model abuse or training data exposure. AI penetration testing adds these AI-specific attack paths and tests them together with the APIs and infrastructure around your AI system.

Can you test our RAG pipeline, not just the model itself?

Yes. GenAI testing covers the ingestion, retrieval and orchestration layers of your RAG pipeline, not just the model endpoint.

Do you test AI agents that take autonomous actions?

Yes. We test how agents use tools, plugins and permissions, including prompt injection that pushes an agent into actions it should not take.

What access do you need from us?

Scoped access to your model endpoints, APIs or staging environment, agreed together during scoping. Production credentials are not needed unless production testing is agreed.

Do you test in production or staging?

Either, depending on what you approve during scoping. Production testing is scheduled separately and has clear limits.

What do we receive when testing is complete, and is retesting included?

A risk-ranked findings report with exploit evidence, prioritized remediation guidance, and a retest to confirm each fix closes the gap.

Is AI penetration testing a one-time engagement or ongoing?

Both are available: a single point-in-time engagement, or continuous testing that follows your release schedule.

Game Changing Resources

Case studies, threat intel, and insights on what continuous, human-led testing looks like in practice.

Evolve Security Joins Anthropic’s Cyber Verification Program

Evolve Security joins Anthropic's Cyber Verification Program, giving OSOC operators full, unthrottled Claude access for authorized red team and AI pen testing.

AI AppSec Champions: How to Build Internal AI Security Expertise Before It’s Too Late

AI security risks like prompt injection and LLM data flows require a new kind of champion. Discover how the AI AppSec Champion model helps engineering teams catch vulnerabilities before they become breaches.

Matt Sharp, CISO, Xactly Corp

In this customer spotlight, Matt Sharp, CISO at Xactly, discusses how AI is reshaping the threat landscape, why Continuous Penetration Testing has become essential for modern security programs, the importance of human-in-the-loop validation, and how Evolve Security helps prioritize the exposures that matter most to reduce business risk.

Webinar: Large Language Models 4 NØØBs

EvolveSec | July 2022 | J. R. Hernandez

Executive Dinner: Offensive Security in the Age of Frontier AI

Carnevor | Milwaukee’s Premier Steakhouse, Milwaukee, United States

Black Hat & Def Con 2026

Las Vegas

Is Anybody Safe? Adaptability in the Age of AI Disruption - with Mark Carney

Is any security company safe from AI disruption? Evolve Security CEO Mark Carney's answer: no and that's the wrong question anyway.

Pen Testing in the Age of AI: Man + Machine w/ Paul Petefish

AI is changing security fast. But is it replacing pentesters, or just giving them a powerful new co-pilot?